Built to handle other people's money with care.
Money
Cards are typed into your processor's own secure fields inside the page. Yahiv only ever receives a token, the card brand and the last four digits — never the full number or the security code.
Every charge is written down before the processor is asked, so a lost connection or a double click can't charge a donor twice or lose a gift.
A refund is reserved before it's sent, so the same money can't be refunded twice. Refunds, voids and deletions above an amount you set can require a second person's OK.
Speed limits, bot checks and hidden traps stop criminals from testing stolen cards on your giving page.
Your data
Every organization's data is kept separate. Each page and every request is checked against your organization, and automated tests check that it stays that way.
Processor, email and text keys are encrypted at rest, and so are ID numbers kept for Israeli receipts. Everything travels over HTTPS.
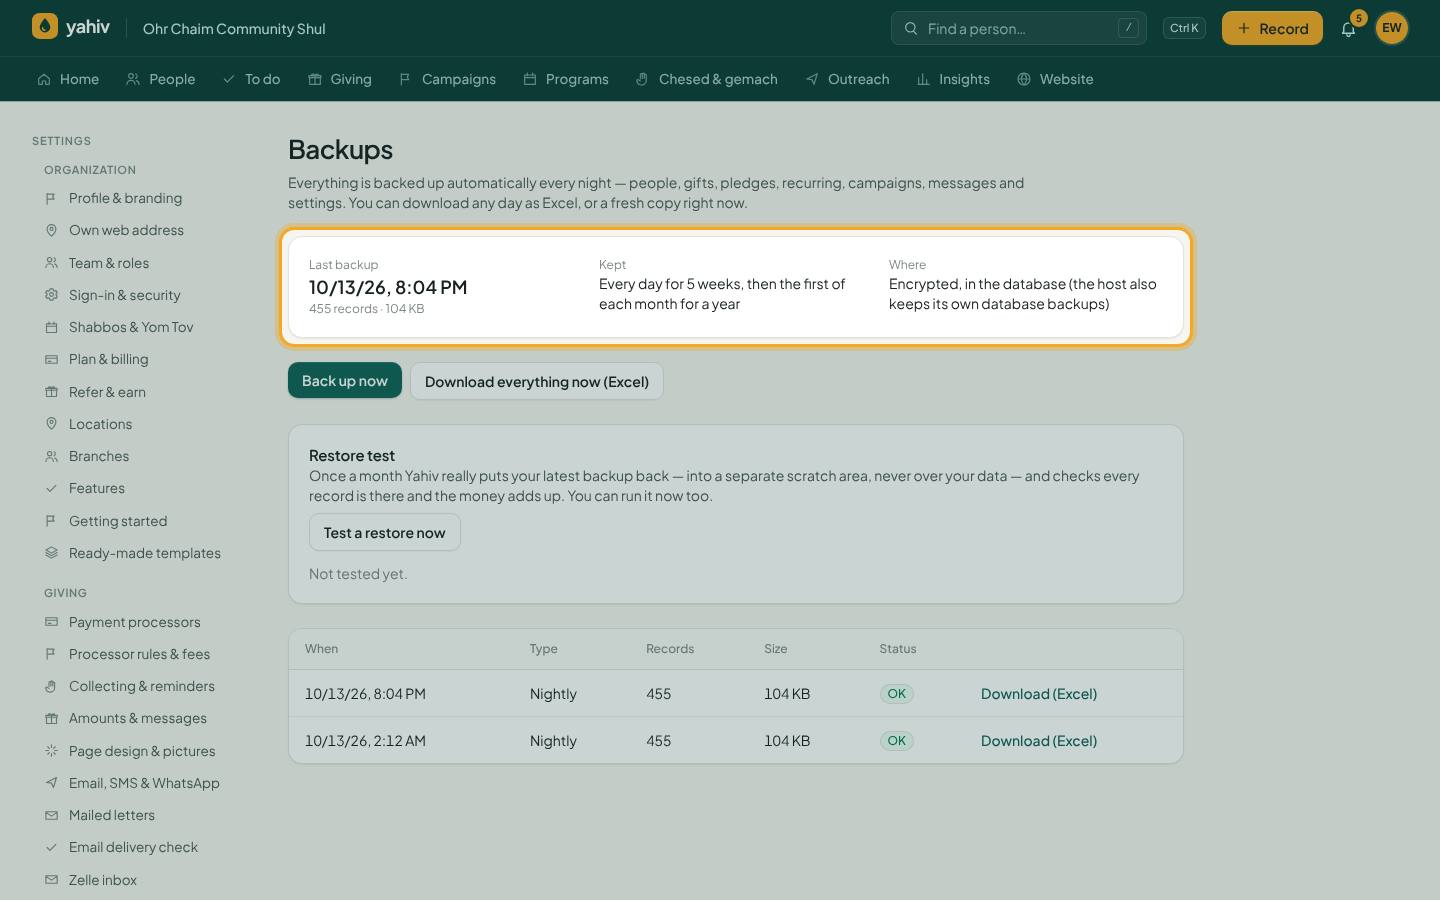
35 days of daily backups plus a monthly one for a year, stored off-site. Download any day as Excel from Settings → Backups.
Every month, each organization's latest backup is restored in a separate area and checked — every record, and the gift and pledge totals.
Bring back deleted people, voided gifts and cancelled pledges.
Who can get in
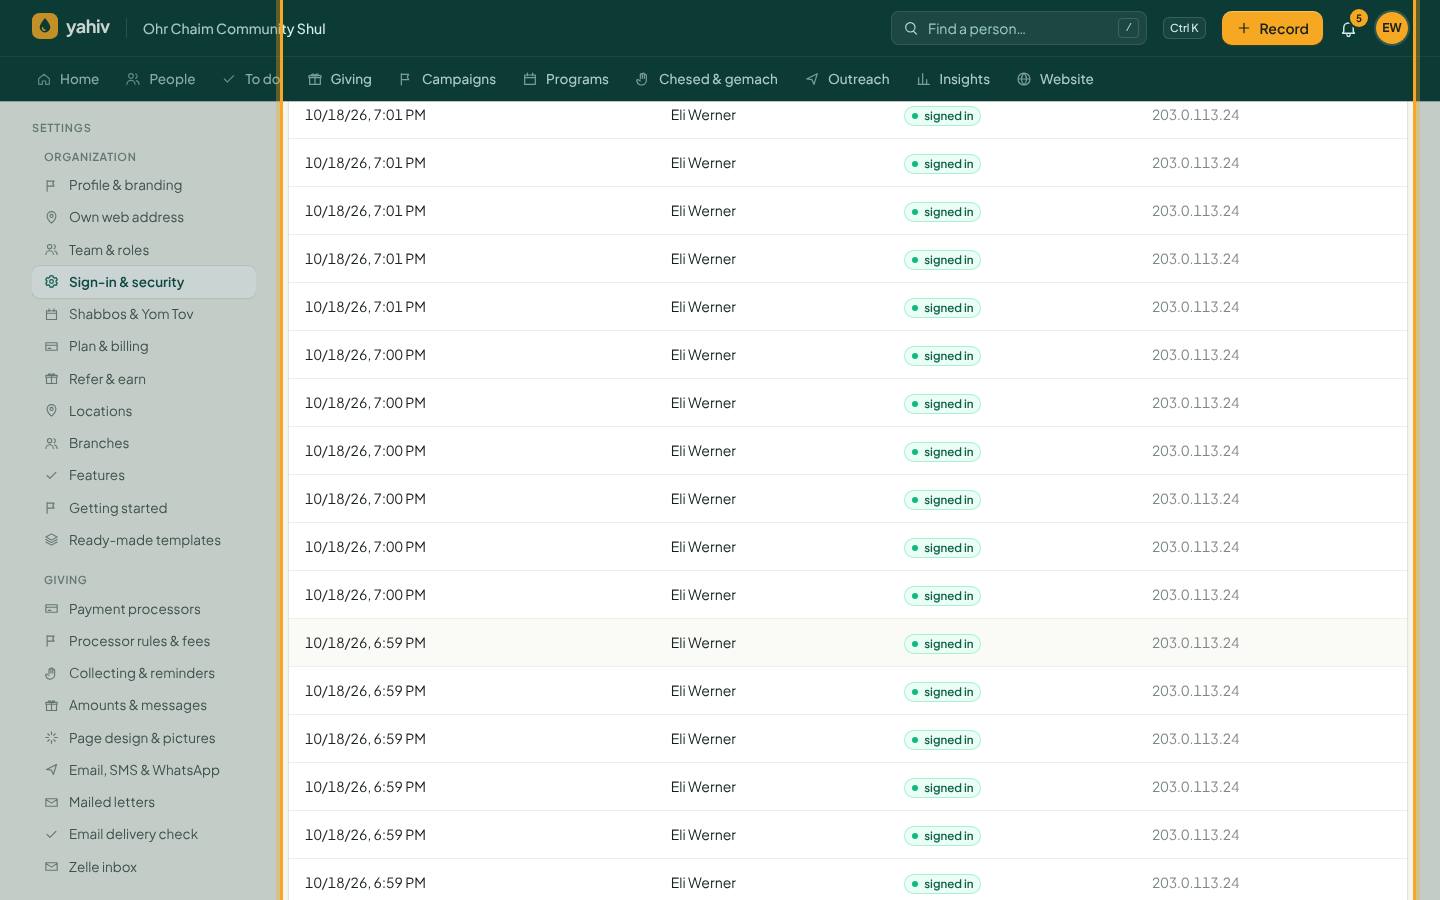
Require a code from an authenticator app for everyone on your team. Sign-in history, a list of open sessions you can sign out, idle sign-out, and a lockout after repeated failed attempts.
For each person you choose what they can see and do: people, giving, refunds, downloads, outreach, reports, their own results only, and which campaigns.
Every sensitive action is recorded: who did what, and when.
Receipts, statements and pay links are signed. Each link works only for its own purpose, and changing it makes it stop working.
See it in the app
How Yahiv is tested
Every update has to pass before it ships.
Browser tests click through the real app the way a user would: giving pages, phone payments, imports, Zelle, events, accounting and more. They all must pass before an update ships.
The full code was reviewed by an outside AI reviewer (38 findings), a second outside reviewer (3 findings), a five-part deep audit (about 65 fixes plus a final round), and a second full outside review after the new upgrades (48 findings, all fixed, with 54 new tests). Every confirmed finding was fixed and covered by a test.
The reviews focused on what matters most: no double charges, no double refunds, no gifts lost, no receipt numbers skipped, correct pledge balances and correct tax treatment.
The importer was checked against real exports so that a move-in is complete and accurate.
What you can do too
- Turn on Require 2-step sign-in for your whole team (Settings → Sign-in & security).
- Never write card numbers in notes, emails or spreadsheets — use the card fields or the donor's update-my-card link.
- Remove team members who leave, and look over the sign-in history now and then.
- Complete your card processor's yearly security questionnaire — because cards never touch Yahiv, it's usually the short one.
Questions about security?
Book a demo and ask us anything — we'll show you each of these in the app.